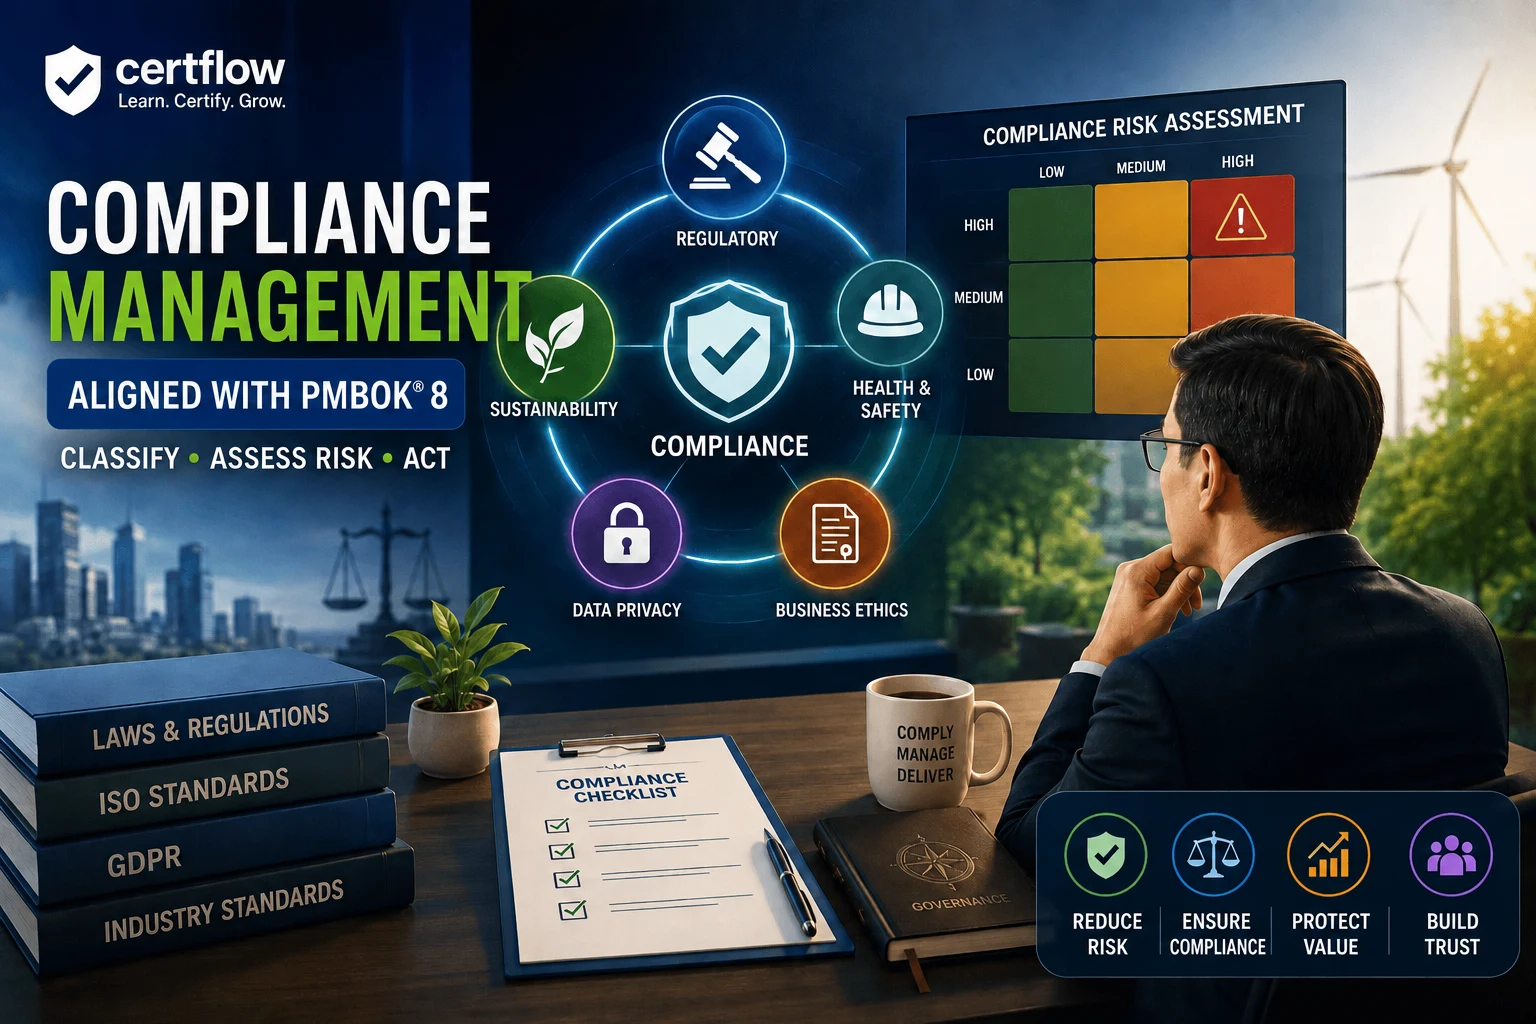
Compliance không chỉ là legal checklist — mà là risk management thực sự. PMBOK 8 tích hợp compliance vào business environment domain. Bài này đi qua cách tiếp cận toàn diện.
1. Tại sao compliance là "non-negotiable"?
Nhiều PM coi compliance là "phần phụ" — thứ gì đó legal team xử lý. Nhưng thực tế, compliance failures là một trong những nguyên nhân hàng đầu dẫn đến project termination.
PMBOK 8 liệt kê compliance trong nhiều contexts: governance framework enforcement, enterprise environmental factors, quality dimensions (conformity), và sustainability integration. Compliance không phải một performance domain riêng — nó xuyên suốt MỌI domain.
PMBOK® 8, Section 1.3.2: Organizational governance includes "enforcing legal, regulatory, and compliance requirements" và "defining ethical, social, and environmental responsibilities." Project governance phải operate WITHIN these boundaries.
Và trong PMP ECO, "Plan and manage project compliance" nằm trong Business Environment Domain — nhấn mạnh rằng compliance kết nối dự án với thế giới bên ngoài: luật pháp, regulations, industry standards, và societal expectations.
2. Compliance trong bối cảnh PMBOK 8
PMBOK 8 không có một chapter riêng cho compliance — thay vào đó, compliance được tích hợp vào nhiều nơi:
Performance Domain | Compliance relevance
|
|---|---|
Governance | "Ensuring compliance with regulatory and legal requirements to maintain organizational accountability" |
Scope | Compliance requirements là PART OF scope — nonfunctional requirements |
Quality | "Conformity" là 1 trong 7 quality dimensions: "Do deliverables comply with regulatory and industry standards?" |
Risk | Noncompliance là risk — threats to compliance phải nằm trong risk register |
Stakeholders | Regulatory bodies là stakeholders — phải được engaged và managed |
Finance | Compliance costs (audits, certifications, training) phải nằm trong budget |
3. Framework 7 enablers quản lý compliance
Nhóm | Enabler | Câu hỏi cốt lõi
|
|---|---|---|
Identify | Confirm compliance requirements | Regulations nào áp dụng cho dự án này? |
Classify | Classify compliance categories | Phân nhóm thế nào cho dễ quản lý? |
Assess | Determine potential threats | Rủi ro nào đe dọa compliance? |
Assess | Analyze consequences of noncompliance | Hậu quả nếu vi phạm là gì? |
Act | Use methods to support compliance | Dùng tools/processes gì để đảm bảo? |
Act | Determine approach and actions | Kế hoạch hành động cụ thể là gì? |
Monitor | Measure extent of compliance | Dự án đang tuân thủ ở mức nào? |
4. Xác nhận và phân loại compliance requirements
Confirm Compliance Requirements
PM phải xác nhận compliance requirements TRƯỚC khi planning bắt đầu — vì chúng ảnh hưởng scope, schedule, cost, và approach. Sources bao gồm: government regulations (federal, state, local), industry standards (ISO, IEEE, HIPAA, PCI-DSS), organizational policies (internal compliance, ethics codes), contractual obligations (SLAs, warranties, IP terms), và international requirements (cross-border data transfer, import/export).
PMBOK 8 Enterprise Environmental Factors liệt kê: "Government or industry standards — regulatory agency regulations related to products, production, environment, safety, quality, and workmanship" và "Public health and safety regulations — government-imposed health protocols, travel restrictions, quarantine measures."
Classify Compliance Categories
Phân loại giúp PM quản lý compliance có hệ thống — mỗi category có different requirements, different owners, different monitoring approaches.
Category | Bao gồm | Ví dụ regulations | Consequence noncompliance
|
|---|---|---|---|
Regulatory / Legal | Laws, government mandates | SOX, GDPR, FDA, building codes | Fines, lawsuits, project shutdown |
Health & Safety | Worker safety, public safety | OSHA, construction safety, hazmat | Injuries, fatalities, criminal liability |
Security | Data, physical, cyber security | PCI-DSS, ISO 27001, NIST | Data breaches, lawsuits, reputation |
Environmental / Sustainability | Environmental protection, emissions | EPA, carbon regulations, waste disposal | Fines, cleanup costs, community opposition |
Industry Standards | Professional/technical standards | ISO 9001, CMMI, IEEE, PMBOK | Quality issues, market rejection |
Contractual | Agreement obligations | SLAs, IP clauses, warranty terms | Penalties, termination, litigation |
Ethical | Professional conduct, fairness | PMI Code of Ethics, anti-corruption | License revocation, reputation damage |
💡 Mẹo PMP: Khi đề thi nêu nhiều compliance categories — đáp án đúng luôn ưu tiên health & safety TRƯỚC, sau đó regulatory/legal, rồi mới đến contractual và standards. Safety of people is ALWAYS the highest priority.
5. Threats to compliance và consequences of noncompliance
Determine Potential Threats
Threat | Mô tả | Ví dụ
|
|---|---|---|
Knowledge gaps | Team không biết regulations nào áp dụng | Developer không biết GDPR áp dụng cho EU users |
Evolving regulations | Regulations thay đổi giữa chừng dự án | Luật bảo vệ dữ liệu mới ban hành sau khi design done |
Cross-jurisdiction complexity | Dự án đa quốc gia với regulations khác nhau | Data residency requirements khác nhau ở EU, US, China |
Resource pressure | Deadline gấp → team cắt bớt compliance steps | Bỏ qua security testing để ship đúng hạn |
Third-party risk | Vendors/subcontractors không comply | Subcontractor vi phạm labor regulations |
Scope creep | Features mới thêm mà không assess compliance impact | Thêm payment feature mà không PCI-DSS compliance |
Ambiguity | Regulations không rõ ràng, nhiều cách interpret | "Reasonable security measures" — reasonable là gì? |
Analyze Consequences of Noncompliance
Level | Consequence | Impact
|
|---|---|---|
Financial | Fines, penalties, lawsuits, cleanup costs | $$$$ — GDPR fines up to 4% global revenue |
Legal | Litigation, criminal charges, injunctions | Project shutdown, personal liability |
Operational | Product recall, rework, redesign | Schedule delay, cost overrun, resource waste |
Reputational | Public trust loss, media coverage, brand damage | Long-term business impact beyond project |
Strategic | Market access denied, partnerships lost | Business opportunity permanently lost |
Human | Injuries, health impacts, community harm | Irreversible — highest priority always |
PMBOK® 8, Section 1.3.1: "The project is terminated for other reasons such as legal, regulatory, or compliance issues." — Noncompliance có thể lead to project termination — not just fines.
6. Methods to support compliance
Proactive Methods — Build compliance IN
- Compliance Requirements Integration — Include compliance as PART OF scope (nonfunctional requirements, acceptance criteria, DoD). Không phải "add-on" mà là "built-in."
- Subject Matter Experts — Engage legal, regulatory, safety SMEs sớm — PMBOK 8 "Apply Expertise" function.
- Training — Đào tạo team về relevant regulations. Knowledge gaps là threat #1.
- Compliance Checklists — PMBOK 8: checklists "ensure that a project or task is ready to start" — compliance checklists cho mỗi phase/sprint.
- Design for Compliance — Architecture decisions tính đến compliance từ đầu: data encryption by default, audit logging, role-based access.
Detective Methods — Find noncompliance early
- Audits — PMBOK 8: Quality audit "identifies good practices, nonconformities, gaps." Regular compliance audits — internal và external.
- Inspections — Verify deliverables meet compliance standards.
- Testing — Security testing, penetration testing, load testing, accessibility testing.
- Reviews — Phase gate reviews include compliance checkpoints: "Do deliverables comply with regulatory and industry standards?"
Corrective Methods — Fix noncompliance
- Change requests — When compliance gaps found, submit CRs to address them.
- Root cause analysis — Why did noncompliance occur? Process gap? Knowledge gap? Pressure?
- Corrective action plans — Timeline, responsible party, verification of fix.
- Escalation — Severe noncompliance escalated per governance framework — immediately for safety/legal issues.
7. Measure compliance — Metrics và monitoring
Compliance Metrics
Metric | Đo cái gì | Target ví dụ
|
|---|---|---|
Compliance completion % | % requirements đã verified | 100% trước go-live |
Open compliance issues | Số issues chưa resolve | 0 critical, <5 medium |
Audit findings | Số nonconformities từ audits | Giảm 20% so với audit trước |
Training completion % | % team đã trained cho relevant regulations | 100% |
Time to resolve | Thời gian từ phát hiện → fix compliance issue | <48 hours cho critical |
Third-party compliance % | % vendors đáp ứng compliance requirements | 100% |
Continuous Monitoring
Compliance monitoring phải là continuous, không phải event-based: regular compliance reviews (mỗi phase hoặc sprint), compliance dashboard (RAG status cho mỗi category), regulatory change monitoring (scan for new/changed regulations), vendor compliance tracking, và incident reporting mechanism.
PMBOK® 8 Check Results, Governance Domain: "Ensuring compliance with regulatory and legal requirements" — đây là outcome bắt buộc của governance domain. PM phải demonstrate compliance at closure.
8. Predictive vs. Adaptive compliance
Aspect | Predictive | Adaptive
|
|---|---|---|
Compliance planning | Detailed upfront, integrated into PM plan | Compliance requirements in DoD, sprint-level checks |
Verification | Phase gate reviews, formal inspections | Sprint reviews include compliance checks, automated testing |
Change impact | Compliance impact analysis for every CR | PO considers compliance when reprioritizing backlog |
Documentation | Formal compliance records, audit trails | Lightweight but sufficient evidence (automated test results, acceptance records) |
Audits | Scheduled formal audits | Continuous — compliance checks built into CI/CD pipeline |
PMBOK 8: "For projects in heavily regulated environments, such as healthcare, there may be phase gates required for regulators to carefully assess" — regulated environments often need predictive elements EVEN in adaptive projects. Hybrid approach: agile development + predictive compliance gates.
9. Tip thi PMP
📍 Tip 1 — Safety FIRST: Khi đề mô tả conflict giữa schedule và safety compliance — safety LUÔN thắng. "Fast-track by skipping safety testing" = ALWAYS wrong. "Delay to ensure compliance" = usually right.
📍Tip 2 — Compliance = scope: Compliance requirements là PART OF scope — nonfunctional requirements. Khi đề nói "team discovers new regulation mid-project" → submit change request to add compliance activities to scope.
📍 Tip 3 — Regulatory bodies = stakeholders: Khi regulatory body issues new requirement → treat as stakeholder management: identify, assess impact, engage, respond. NOT ignore or defer.
📍Tip 4 — Noncompliance escalation = immediate: Khi đề mô tả "team discovers potential regulatory violation" → escalate immediately per governance framework. Do NOT investigate first, do NOT wait for next meeting.
10. Mười câu hỏi trắc nghiệm tình huống
Question 1
Your e-commerce project is expanding to the European market. Two weeks before launch, a developer discovers that user data handling doesn't comply with GDPR. The PM says: "We'll fix it in the next release."
Is the PM's approach correct?
A. Yes — ship now, fix later to meet the deadline.
B. No — GDPR noncompliance exposes the organization to fines up to 4% of global revenue. Delay the launch, address GDPR compliance first, then launch when compliant. Compliance is non-negotiable.
C. Launch in non-EU markets first while fixing GDPR.
D. Get legal to sign a waiver accepting the risk.
Question 2
A construction project's safety officer reports that a subcontractor's workers are not wearing required fall protection at 20 feet. The subcontractor says: "We always work this way — it's faster."
What should you do FIRST?
A. Document the violation and discuss at the next safety meeting.
B. Stop the unsafe work IMMEDIATELY, ensure workers have proper fall protection, then investigate root cause and implement corrective actions with the subcontractor.
C. Issue a formal warning to the subcontractor.
D. Report to OSHA and let them handle it.
Question 3
Your agile software project adds a payment feature in Sprint 7. The team builds it quickly without considering PCI-DSS compliance. Sprint review: the PO loves it.
What compliance risk was created?
A. No risk — the PO accepted the feature.
B. Scope creep introduced a compliance gap. Payment features require PCI-DSS compliance (data encryption, access controls, audit trails). The feature must NOT be released until compliance is verified. The DoD should include compliance checks for any feature handling sensitive data.
C. PCI-DSS only applies to payment companies, not e-commerce.
D. Compliance can be added in a future sprint.
Question 4
A pharmaceutical project is in Phase 2 clinical trials. New FDA guidance is published that changes data submission requirements. The team has already collected 6 months of data under old requirements.
What should you do?
A. Continue under old requirements since the project started before the change.
B. Assess the impact of new guidance on existing data and future collection, consult regulatory affairs SME, develop a compliance plan, submit a change request if scope/schedule/cost are affected, and communicate with the FDA about transition approach.
C. Start over with new requirements.
D. Wait for FDA to formally mandate the change.
Question 5
Your project's compliance audit reveals 3 minor findings and 1 major finding related to data access controls. The auditor gives 30 days to remediate. The PM has addressed the 3 minor findings but says the major finding "requires too much rework — we'll accept the risk."
Is this approach acceptable?
A. Yes — risk acceptance is a valid strategy.
B. No — a MAJOR audit finding related to data access controls likely involves regulatory requirements that cannot be "risk accepted" by the PM. Escalate to sponsor and compliance team, develop a remediation plan, and address within the 30-day window.
C. Request an extension from the auditor.
D. Document the decision and move on.
Question 6
Your project outsources data processing to a vendor in another country. The vendor's data center doesn't meet your organization's security standards, but their prices are 40% lower.
What compliance consideration is MOST critical?
A. The cost savings justify accepting lower security standards.
B. Third-party compliance is the PM's responsibility. Verify the vendor meets ALL applicable security and data protection requirements (including cross-border data transfer regulations). Lower cost does NOT justify noncompliance.
C. Add security requirements to the contract and trust the vendor to comply.
D. Use the vendor for non-sensitive data only.
Question 7
Your team is under intense pressure to deliver by quarter-end. The QA lead says: "We need 2 more weeks for security testing." The sponsor says: "Ship now — we'll patch any issues."
How should you handle this?
A. Follow the sponsor's direction — they have authority over the project.
B. Present the compliance risk transparently: what specific security tests are pending, what vulnerabilities might exist, what the consequences of a breach could be (fines, data loss, reputation), and recommend the sponsor make an informed decision with full visibility of the risk.
C. Ship a limited release without sensitive features.
D. Document the sponsor's decision and ship as directed.
Question 8
Your organization operates in 5 countries. Each has different environmental regulations for waste disposal from your manufacturing project. Tracking compliance across all jurisdictions is becoming overwhelming.
What approach should you take?
A. Comply with the strictest country's regulations — that covers all others.
B. Create a compliance matrix categorizing requirements by jurisdiction, identify common requirements versus jurisdiction-specific ones, assign ownership for each, and establish monitoring for regulatory changes across all 5 countries.
C. Hire a compliance consultant for each country.
D. Delegate to local teams and trust their knowledge.
Question 9
During a sprint retrospective, a developer admits they bypassed the code review process to meet a deadline. The bypassed code handles patient health data in a healthcare application.
What is the compliance implication?
A. No issue — the code works and tests passed.
B. Bypassing code review for health data handling is a HIPAA compliance risk — unreviewed code may contain vulnerabilities exposing protected health information. Conduct immediate code review, assess any data exposure, implement controls to prevent bypassing reviews for compliance-sensitive code, and address the cultural pressure that led to the bypass.
C. Add the code review to the next sprint's tasks.
D. The developer should be reprimanded for not following process.
Question 10
At project closure, you discover that environmental compliance documentation for the construction project is incomplete. The operations team needs this documentation for ongoing compliance reporting to regulators.
What should you do?
A. Close the project — documentation can be completed by operations.
B. Delay closure until compliance documentation is complete. Transfer verified and complete compliance records to the operations team. Incomplete compliance documentation creates regulatory risk for the organization beyond the project.
C. Archive what exists and note the gap in lessons learned.
D. Ask the regulatory compliance team to complete the documentation.
Đáp án
Question 1: Answer: B
— GDPR violations carry severe penalties. "Fix later" creates legal exposure from Day 1. PMBOK 8: compliance with regulatory requirements is a governance outcome. Launching non-compliant is not a PM decision to make — it requires sponsor/legal sign-off at minimum, and most organizations would not accept this risk.
Question 2: Answer: B
— Safety compliance is IMMEDIATE — people's lives are at risk. PMBOK 8: safety is the highest priority. Stop the hazard FIRST, then investigate and correct. Documentation (A) and warnings (C) are too slow when lives are at stake.
Question 3: Answer: B
— PCI-DSS applies to ANY system handling payment card data. PO acceptance doesn't override compliance requirements. PMBOK 8: compliance is part of scope. Adding features without compliance assessment = compliance gap. DoD should include "meets applicable regulatory requirements."
Question 4: Answer: B
— Regulatory changes mid-project require systematic assessment. The PM should engage SMEs, assess impact, plan response, and communicate proactively. Ignoring (A) risks rejection at approval. Starting over (C) may be excessive — some existing data may be compliant. Waiting (D) is passive and risky.
Question 5: Answer: B
— Risk acceptance for compliance issues is different from project risks. Major findings, especially related to data security, typically involve regulatory obligations that cannot be waived by the PM. The PM should escalate — this is a governance decision, not an operational one.
Question 6: Answer: B
— Third-party risk is a major compliance threat. PMBOK 8: the PM must ensure vendor compliance. Cost savings never justify regulatory noncompliance. Contractual clauses (C) alone aren't enough without verification and monitoring. The PM must verify, not just trust.
Question 7: Answer: B
— PMBOK 8 Be an Accountable Leader: "integrity — willingness to share bad news early." The PM must present the compliance risk transparently — the sponsor can still decide to ship, but it must be an INFORMED decision, not an uninformed one. Documenting without informing (D) is CYA, not leadership.
Question 8: Answer: B
— PMBOK 8 ECO: "classify compliance categories." A structured approach (compliance matrix) makes multi-jurisdiction compliance manageable. Strictest standard (A) may not cover jurisdiction-specific requirements (e.g., specific reporting formats). Local delegation (D) without central coordination risks gaps. A matrix provides visibility and accountability.
Question 9: Answer: B
— Healthcare data = HIPAA compliance. Bypassing quality processes for compliance-sensitive code creates regulatory risk. PMBOK 8: "Embed Quality Into Processes and Deliverables." The fix is both technical (review the code NOW) and systemic (prevent bypass, address deadline pressure). Reprimanding (D) without fixing the system doesn't prevent recurrence.
Question 10: Answer: B
— PMBOK 8 closure: "Verify that all contractual, regulatory, legal, social, and environmental obligations have been met." Incomplete compliance documentation = unfulfilled closure criterion. The PM should not close until regulatory obligations are documented and transferred. This protects both the project AND the organization.
11. Tổng kết
Compliance management kết nối dự án với thế giới bên ngoài — luật pháp, regulations, safety standards, và societal expectations. Ba takeaways:
- Compliance is scope, not an add-on — Regulatory requirements, safety standards, data privacy, environmental obligations — tất cả đều là nonfunctional requirements thuộc về scope. PM phải integrate compliance vào planning từ ngày đầu, không phải "thêm vào" khi gần go-live. PMBOK 8: "conformity" là 1 trong 7 quality dimensions.
- Safety ALWAYS wins over schedule — Khi conflict giữa deadline và compliance — compliance thắng, đặc biệt health & safety. PM phải present trade-offs transparently để sponsor ra informed decision. "Ship now, fix later" cho compliance = gambling with the organization's future.
- Classify, monitor, escalate — 7 compliance categories, mỗi cái có different owners, different consequences, different monitoring approaches. Compliance matrix giúp quản lý có hệ thống. Continuous monitoring — không phải "check once then forget." Và khi violations xảy ra — escalate immediately per governance framework, đặc biệt safety và legal issues.
PMBOK® 8, Section 3.7: "By integrating sustainability into project management, organizations can align with the triple bottom line — balancing social equity, environmental stewardship, and economic prosperity." Compliance là nền tảng để đạt được triple bottom line — không có compliance, sustainability chỉ là slogans.
Câu Hỏi Thường Gặp (FAQ)
Compliance risk trong dự án khác business risk như thế nào?
Business risk: không đạt objectives, cost overrun, schedule delay — có thể accept, transfer, hoặc mitigate theo risk appetite. Compliance risk: vi phạm regulations, laws hoặc standards — không thể ignore hay accept đơn giản. Hậu quả: fines, legal action, project shutdown, reputational damage. Compliance risk cần được identify sớm và có compliance plan rõ ràng.
PMBOK 8 tiếp cận sustainability và ESG compliance như thế nào?
PMBOK 8 bổ sung Environmental, Social, và Governance (ESG) considerations vào business environment analysis. PM cần xem xét: environmental impact của project outputs, social impact lên stakeholders và community, và governance standards của tổ chức. ESG compliance ngày càng quan trọng, đặc biệt với international projects và publicly listed companies.
Khi project audit phát hiện non-compliance, PM xử lý thế nào?
Process: (1) Acknowledge findings — không defensive. (2) Root cause analysis — tại sao non-compliance xảy ra? (3) Develop Corrective Action Plan với timeline cụ thể. (4) Escalate đến Sponsor và PMO. (5) Implement corrections. (6) Verify remediation. (7) Document lessons learned để prevent recurrence. PMBOK 8: transparency quan trọng hơn self-protection.
Bạn đã nắm vững quản lý compliance dự án — giờ là lúc luyện tập với câu hỏi thi thật.
Bài tiếp theo: Quản Lý Thay Đổi Dự Án: Change Control Process từ A-Z
Nguồn tham khảo chính thức:
Bạn đã sẵn sàng luyện tập chưa?
Thử CertFlow miễn phí — 10 câu hỏi, không cần đăng ký.
Bắt Đầu Miễn Phí